Mass Assignment: The API Vulnerability That Can Turn Users Into Admins
An attacker submits an API request that looks completely normal, except they've added a single field: "role": "admin" or "ownerId": 999. The web framework automatically maps request data to your internal object model, so it binds and saves that field. The attacker is now an administrator. They never stole credentials or bypassed authentication. They just modified a property the API should never have exposed in the first place.
This is mass assignment, and it remains one of the easiest vulnerabilities to introduce and hardest for automated tools to detect because it depends on business logic. Manual penetration testing uncovers it where scanners fall short.
What Is a Mass Assignment Vulnerability?
Mass assignment occurs when user-controlled input can update object properties that were never intended to be externally writable.
The core problem is simple: a framework takes incoming request data and automatically updates your object model with whatever fields are included. If the request contains a role field, the framework binds it to your user object's role property. No explicit permission checks or validation of the fields that should be writable, just automatic field mapping.
This happens because developers use frameworks that automatically bind incoming data to model properties to save time and reduce boilerplate code. It works great when you control all the incoming data. It becomes a security hole when API clients (or attackers) can decide which fields to send.
Related Vulnerabilities
Mass assignment often overlaps with broken access control, but they protect different boundaries. Broken object-level authorization checks whether a user can access a specific resource they own. Mass assignment checks whether a user can modify resource properties they shouldn't be able to change. A developer might correctly prevent user A from reading user B's profile but fail to prevent user A from setting their own role field to admin.
Mass assignment also differs from insecure deserialization, HTTP parameter pollution, and direct object reference attacks. It specifically involves automatically binding request parameters to model properties without an explicit allowlist.
How a Mass Assignment Attack Works
The attack path is straightforward: an attacker modifies an otherwise valid API request by adding properties that weren't exposed in the official API documentation or frontend form.
Automatic Data Binding
Modern web frameworks (Rails, Django, Spring, Express, Laravel) offer automatic object binding to reduce boilerplate code. When a request arrives, the framework inspects the incoming JSON or form data and automatically maps each key to a corresponding model property. If the model has a property named role, the framework looks for a role field in the request and assigns it.
This behavior is invisible to the API consumer. The frontend application might only show fields the developer intended to be writable, such as name, email, and bio. But if the underlying model contains properties such as role, isAdmin, ownerId, or accountStatus, the framework will happily bind and persist those fields if an attacker includes them in the request.
Unauthorized Field Changes
An attacker intercepts or crafts an HTTP request with added fields. A normal request might look similar to this:
- POST /api/users/profile {"name": "Alice", "email": "alice@example.com", "bio": "Engineer"}
The attacker modifies it to:
- POST /api/users/profile {"name": "Alice", "email": "alice@example.com", "bio": "Engineer", "role": "admin"}
The framework binds all fields, including role, and updates the user object. The attacker's role is now admin. If the application trusts the role field for authorization checks, the attacker immediately gains elevated privileges.
Exploitation often targets less obvious fields: ownerId to claim resource ownership, status to bypass workflow restrictions, accountTier to unlock premium features, or discountPercentage to alter pricing. The field names come from code inspection, API documentation leaks, or trial-and-error testing.
Why Mass Assignment Vulnerabilities Matter
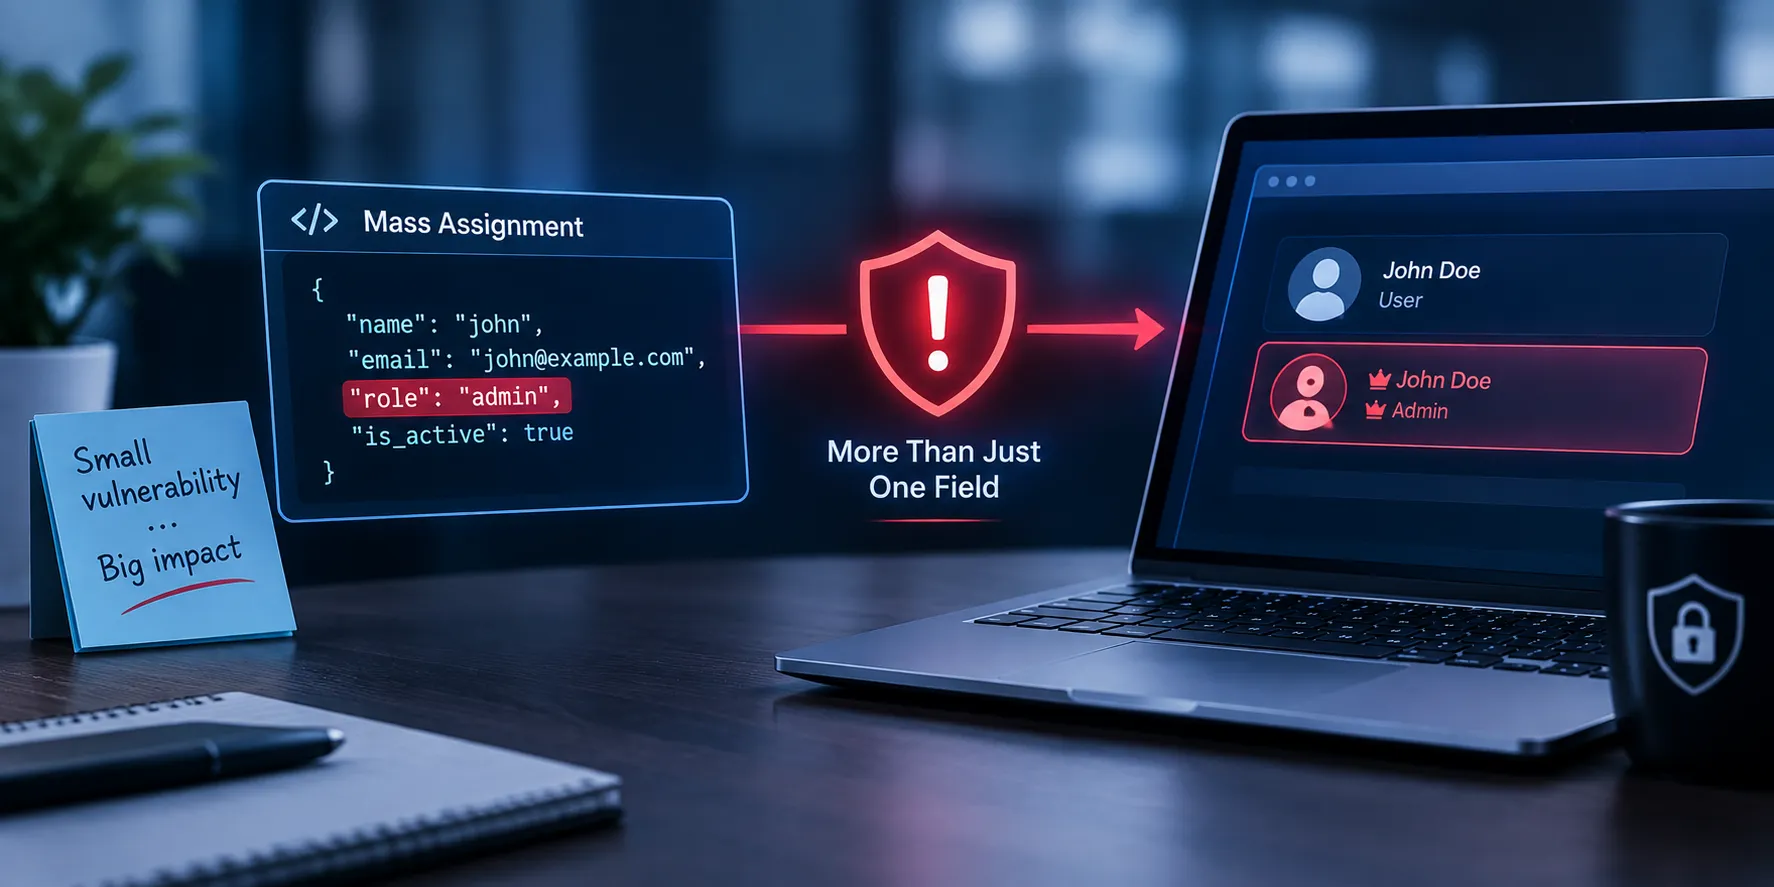
Mass assignment vulnerabilities persist because developers make predictable implementation mistakes, and generic scanners often miss business-sensitive fields. The severity isn't uniform across all affected fields. Exposing a cosmetic property is low risk. Exposing a privilege or ownership field can compromise your entire authorization model. Understanding why the vulnerability occurs and what damage it enables is the foundation for detection and prevention.
Common Root Causes
Developers bind external input directly to domain models without filtering. They rely on hidden form fields instead of server-side authorization and assume attackers won't discover undocumented fields. Developers may misconfigure ORM settings or fail to use explicit data-transfer objects (DTOs) that define request contracts. Nested objects compound the problem: an attacker modifying user.organization.isPrivate might succeed even when top-level fields are protected.
Security and Business Impact
The severity of mass assignment depends on which fields are exposed.
- Changing a user's displayName is low risk.
- Changing their role to admin is critical.
- Changing an order's totalPrice to zero breaks billing.
Mass assignment enables privilege escalation, unauthorized ownership changes, workflow manipulation, data integrity loss, and unauthorized configuration updates. In multi-tenant systems, an attacker might modify tenantId to access another organization's data. In e-commerce applications, they might change paymentProcessed to bypass payment.
In IoT systems, modifying device configuration fields through an API can disable security controls or reroute traffic. That's why IoT security testing that includes manual API review is essential. Automated scanning won't reveal what an attacker can actually do when they modify device fields.
How to Detect Mass Assignment
Code and Schema Review
Review the request models, serializers, and controllers that handle incoming data. Identify which model properties can be directly bound to external input. Check ORM configuration for unrestricted property assignment. Inspect API schemas and frameworks for automatic binding behavior.
Look for code patterns such as:
- Direct assignment of request parameters to model properties
- DTOs that inherit from domain models
- Frameworks configured to bind all matching fields
- Absence of field-level authorization checks
Manual API Testing
A tester documents all legitimate API fields, then systematically tests additional fields across different user roles. They will:
- Test POST, PUT, and PATCH requests.
- Try modifying nested properties.
- Verify that the system rejects or logs sensitive changes.
- Observe whether unauthorized field modifications succeed silently, are rejected with an error, or are accepted and persisted.
Only authorized testing in a controlled environment reveals which fields are actually writable and which roles can modify them.
Automated scanners can't tell you which fields matter. A scanner might detect that your API accepts a discountCode field and flag it as a potential mass-assignment vulnerability. But does that field actually affect anything? Is it validated server-side? Does it break your business logic or just get silently ignored? Only manual testing answers these questions. That gap between 'this field exists' and 'this field is actually dangerous' is where mass assignment vulnerabilities hide.
How to Prevent Mass Assignment
Prevention requires explicit input contracts and server-side authorization.
Explicit Input Models
Never bind external input directly to persistent domain models. Use data-transfer objects (DTOs) or request-specific schemas that explicitly list acceptable fields for each request type. Map incoming data to these allowlisted DTOs, then selectively copy properties to the domain model only after authorization checks pass.
Frameworks such as Spring Data REST, Django REST Framework, and Rails provide tools for explicit mapping. Define separate DTOs for create, update, and admin-only operations. A user update DTO might allow name, email, and bio. An admin update DTO might also allow role and accountStatus.
Field-Level Authorization
Apply authorization at the property level, not just at the endpoint level. A user can access the "/api/users/123/profile" endpoint, but only certain fields should be writable. Check permissions before allowing changes to sensitive properties.
Type and format validation cannot replace authorization. Validating that role is a string does not prevent unauthorized role changes.
Security Verification
Add negative tests that deliberately submit unexpected fields and verify they're rejected. Test role-based behavior across create, read, update, and delete operations. Log all rejected property assignments to prevent attackers from silently modifying fields. Manually review high-risk endpoints where property changes affect privileges, ownership, or pricing.
Frequently Asked Questions
Is mass assignment the same as SQL injection?
No. Mass assignment occurs when an application lets user-controlled request parameters modify object properties that shouldn't be writable. SQL injection involves manipulating SQL queries through unsanitized database input. They are different vulnerabilities.
What is a mass assignment vulnerability?
A mass assignment vulnerability occurs when an API request includes extra fields, and the framework updates them without permission. Send {"role": "admin"}, and it actually updates your role field.
Is mass assignment the same as broken object-level authorization?
No, mass assignment isn't the same. Object-level authorization is about whether you can access a resource at all. Mass assignment is about which fields of that resource you're allowed to change.
Which frameworks can be affected by mass assignment?
Pretty much any framework can be affected by mass assignment if it's not configured carefully. Rails, Django, Spring, Laravel, Express: the vulnerability isn't the framework's fault; it's the developer not restricting what fields can be bound.
Can input validation prevent mass assignment?
No, input validation won't prevent mass assignment. Validation only checks whether the data looks correct. It doesn't stop you from including fields you shouldn't be able to change. You need to allowlist the fields that are writable explicitly.
How is mass assignment tested during a penetration test?
During pentesting, Software Secured documents all the legitimate fields your API accepts, then tries adding fields that shouldn't exist. We test whether we can change them, whether the changes persist in the database, and what happens when different user roles try it.
Ready to get in touch? Get started by booking a consultation now.
About the author
Kaycie Waldman
Demand Generation Manager
Kaycie Waldman works closely with SaaS, cloud, and technology organizations on security, risk, and compliance initiatives that support growth and enterprise readiness. Her work spans strategic content, go-to-market initiatives, and customer trust programs designed to support scale, compliance, and enterprise sales.